Home

Looking for Node.js Developers in Canada? Here’s How to Hire the Best 

Looking for Node.js Developers in Canada? Here’s How to Hire the Best 

Join our Newsletter!

Hire NodeJS Developers in Canada

Are you looking for a skilled Node.js developer in Canada to bring your project to life? Do you need a reliable expert who can build fast, scalable, and high-performing applications? Finding the right developer can be challenging, but with the right approach, you can hire a top Node.js professional who fits your needs perfectly.

Hiring a skilled Node.js developer in Canada is essential for businesses looking to build fast, scalable, and efficient applications. With its non-blocking architecture and real-time capabilities, Node.js is a powerful choice for web and software development. Whether you’re developing a dynamic website, an API-driven platform, or a complex enterprise solution, finding the right developer ensures seamless performance and long-term success. Understanding the key factors in hiring a Node.js expert will help you make an informed decision and achieve the best results for your project.

Let’s explore how you can make the best choice!

Steps to Hire Node.js Developers in Canada

1. Define Your Project Requirements

To hire the right Node.js developer, you must first define your project’s technical and business needs. Outline the core functionalities, expected performance, and scalability requirements of your application. Identify the frameworks and tools you want to use, such as Express.js, Nest.js, or MongoDB, and specify whether the role requires front-end expertise alongside back-end development. Additionally, determine the level of experience required—junior developers handle basic tasks, mid-level developers work on feature-rich applications, while senior developers manage architecture and complex integrations. Having a well-documented project scope ensures that candidates understand your expectations from the start. A detailed job description outlining skills, responsibilities, and project goals will help attract the right talent. Without clarity, the hiring process can become inefficient, leading to mismatches in skills and expectations. A structured approach helps filter candidates early and ensures that only those with relevant expertise apply.

2. Source Qualified Candidates

Finding skilled Node.js developers in Canada requires using multiple recruitment channels. Start by posting job listings on platforms like LinkedIn, Indeed, and Glassdoor, which are popular among Canadian job seekers. Consider using tech-specific job boards such as Stack Overflow Jobs or GitHub Jobs to target professionals with strong development experience. Additionally, networking within Canada’s growing tech community can help you connect with skilled developers—attend industry conferences, local meetups, and online forums to discover potential candidates. If you prefer a more streamlined approach, working with tech recruitment agencies can save time by providing pre-screened candidates. Another option is hiring freelancers through platforms like Toptal or Upwork but ensure that remote hiring aligns with your business needs and legal considerations. A strong sourcing strategy increases the likelihood of finding a developer who meets both your technical and cultural requirements, ensuring a smoother hiring process.

3. Conduct Technical Screening

After gathering applications, the next step is to assess candidates based on their technical skills and experience. Start with a resume review, focusing on past projects, relevant experience, and familiarity with the required Node.js frameworks. Candidates should demonstrate hands-on experience in building scalable applications, working with APIs, and optimizing back-end performance. To ensure technical proficiency, conduct coding assessments through platforms like HackerRank or Codility. These tests evaluate problem-solving abilities, efficiency in writing clean code, and understanding of Node.js fundamentals. Additionally, assess candidates’ experience with database management, security best practices, and cloud-based deployments. An effective screening process filters out underqualified applicants early, allowing only the most capable developers to move forward. By implementing structured assessments, you can streamline hiring and ensure that your chosen developer has the technical expertise necessary to contribute effectively to your project.

4. Assess Technical and Problem-Solving Skills

Once candidates pass the initial screening, conduct in-depth technical interviews to evaluate their problem-solving abilities. Ask questions about key Node.js concepts such as asynchronous programming, event-driven architecture, API development, and database management. Provide real-world scenarios related to your project and assess how they would approach challenges. A practical coding exercise or take-home assignment can help evaluate their thought process and coding efficiency. In addition to technical expertise, consider their ability to design scalable solutions and optimize application performance. Discuss their experience with DevOps practices, cloud computing, and microservices architecture if relevant to your project. Soft skills are equally important—effective communication, adaptability, and teamwork play a significant role in long-term success. The goal is to hire a developer who not only writes efficient code but also collaborates well with your team and adapts to evolving project needs.

5. Make the Right Hiring Decision

After evaluating technical skills, problem-solving abilities, and soft skills, the final step is making an informed hiring decision. Compare candidates based on performance in technical interviews, problem-solving assessments, and cultural fit. Strong communication and teamwork are crucial, as developers often collaborate with designers, project managers, and other team members. Additionally, check references to validate past work experience and reliability. When making an offer, consider industry-standard salaries in Canada and ensure compliance with local labor laws. Offering a competitive package, including professional development opportunities and flexible work arrangements, can help attract top talent. If hiring full-time isn’t feasible, explore freelance or contract-based options. A well-structured hiring process ensures you bring in a skilled Node.js developer who aligns with your technical needs and business goals, setting your project up for long-term success.

Looking to hire top Node.js developers in Canada? At Mindpath, we provide skilled developers who specialize in building high-performance, scalable applications tailored to your business needs. Whether you need full-time developers or project-based support, our experts ensure seamless development with industry-leading technologies.

Let’s bring your vision to life! Contact Mindpath today to hire the best Node.js talent for your next project.


Frequently Asked Questions

Support Is One Click Away

Featured Posts

Related Post

Large language models

Artificial intelligence has become one of the trending topics of discussion in the domain of technology, largely due to LLMs. Large language models or LLMs have made it possible to talk with AI and complete different types of actions, such as generating content or writing code. The impact of LLMs has not only redefined the conventional norms for interacting with technology but also provided new perspectives on information processing. Therefore, more people want to learn about LLMs and how they work. Let us discover how LLMs have become a powerful force in the AI landscape with an overview of their fundamentals.

Want to turn the power of LLMs into real business value? Discover Mindpath’s LLM Development Services to develop intelligent applications that automate workflows, enhance customer experiences, and improve productivity.

What are Large Language Models?

The obvious questions on the mind of any beginner are “What are Large Language Models?” and how they work. You can think of them as AI models which use deep learning, a sophisticated form of machine learning that leverages neural networks. Neural networks are a type of computational system designed along the lines of the human brain, with the interconnected layers represented neurons. LLMs rely on deep learning as it helps in finding intricate patterns in massive training datasets.

The definition in any Large Language Models beginner guide also focuses on the size of LLMs. You must know that the “Large” in LLMs is not an exaggeration as LLMs are built by training on large amounts of data. The data used to train LLMs is obtained from various sources, including the internet, books and many other sources of information. The large amount of training data ensures that LLMs have capabilities for recognizing, translating, predicting and generating human-like text.

Want to customize a large language model for your specific use case? Explore our OpenAI Fine-Tuning API tutorial to learn how to fine-tune LLMs for better accuracy and performance.

How Do Large Language Models Work?

The features of LLMs create questions about the special component that makes them so powerful. Most of the answers to “what is LLM?” focus on the transformer architecture and the attention mechanism. Transformer architecture refers to a neural network design created to process sequential data like text. Conventional models experienced troubles in learning the long-range dependencies in sentences. However, transformers changed the game by introducing the self-attention mechanism.

Almost every LLM definition sheds light on the impact of the self-attention mechanism on the working of LLMs. Self-attention mechanism of transformer architecture measures the significance of different words in a sentence with respect to each other, irrespective of their position. It helps in improving contextual understanding, which serves useful in generating coherent and relevant text.

The design of the transformer architecture involves an encoder and decoder. The encoder transforms the input text into numerical representations, which capture the syntax and semantic meaning of the input text. Subsequently, the decoder uses the numerical representation to craft the output sequence, on the basis of the context offered by the encoder.

Curious how large language models understand context and relationships between words? Discover our attention mechanism explained blog to learn the core concept that powers modern LLMs.

How Do LLMs Learn to Respond to Instructions?

Do LLMs work only with the data used for their training? The basic explanation for LLM means that it uses massive amounts of data in its training. However, it is only the initial stage of training, where the LLM gains general understanding of language from different datasets. The process is known as pre-training and involves subjecting an AI model to unsupervised learning. Pre-training empowers AI models to predict the next word in a sentence based on the preceding words. The pre-training process helps the LLM in understanding grammar, factual knowledge, statistical patterns and syntax of language.

Another crucial process that you may come across in a large language model tutorial is fine-tuning. Once the pre-training process is complete, you can use fine-tuning to prepare the model for domain-specific tasks. Fine-tuning involves the use of smaller datasets focused on the corresponding domain to optimize language models for certain tasks. For instance, you can fine-tune an LLM to serve support for medical diagnosis or creation of legal document summaries.

Prompt engineering is also another notable element in the world of LLMs as it focuses on creating effective instructions. You can take any introduction to LLMs and find insights on the significance of prompt engineering. The best thing about prompt engineering is that you can craft effective instructions to draw desired outputs from LLMs. With prompt engineering, you can teach language models how to work on new tasks without an extensive overhaul.

Concerned about how AI will impact careers and job roles in technology? Explore how AI is redefining job roles in tech to learn how professionals can adapt and stay competitive.

Key Concepts of Large Language Models

As a beginner, you must know some of the most crucial concepts required to work with LLMs. The essential concepts related to LLMs that you should learn before using the models include tokens, embeddings, context window, temperature and model parameters. Let us discover more about the significance of these concepts for LLMs.

1. Tokens

A review of different examples of LLMs will help you know that language models break down text into smaller units. The small units or tokens can be words or characters in the sentence, represented as numbers. Tokens help language models understand natural language and respond to user queries.

2. Embeddings

Embeddings are the numerical representation of tokens, which capture their semantic meaning. Words with similar meaning will have embeddings close to each other in a multi-dimensional space. The embeddings help the model understand the context and relationship between different words in text.

3. Model Parameters

Another important addition among concepts of LLM for beginners points at model parameters. The model parameters are the weights and biases in a neural network, capable of encoding the complete knowledge of the model. New LLMs come with billions and some with trillions of parameters. Adding more parameters improves the performance of LLMs albeit with the burden of increasing demand for computational resources.

4. Context Window

The context window represents the maximum amount of text that the model can evaluate at once. You can think of the context window of a LLM as its short-term memory as the model does not take information outside the context window for the current processing step.

5. Temperature

The description of different large language models examples also showcases the importance of temperature for language models. Temperature is responsible for determining the level of creativity and randomness in the output of language models. Lower temperatures lead to creation of deterministic models while higher temperature introduces more randomness, leading to creative responses. However, higher temperature also means that the responses may be less predictable.

Looking for efficient ways to adapt large language models without high computational costs? Explore our Low-Rank Adaptation (LoRA) blog to learn how lightweight fine-tuning improves LLM performance.

Real-World Applications of LLMs

The popularity of LLMs can be attributed to the growing number of their use cases in the real world. As the capabilities of LLMs continue to expand and evolve, they can serve as key ingredients for innovation in any industry. The following real-world applications of LLMs can help you measure their significance in the domain of technology.

1. Customer Support Chatbots

One of the notable examples which serve the ideal answer to ‘why are large language models’ is the broad range of advanced chatbots and virtual assistants. LLMs can power chatbots to provide automated and personalized customer support anytime. The capabilities of language models help chatbots in answering complex queries and streamlining customer service operations through contextual understanding and sentiment analysis.

2. Content Generation

LLMs are also popular in the field of content generation, ranging from essays to marketing materials. You can find examples of language models like ChatGPT serving millions of users with content creation benefits. Language models can accelerate the content creation process by providing ideas, initial drafts or even creating new content from scratch.

3. Coding

The use cases of LLMs in the real world also draw attention towards their applications in generating code. One of the notable examples of language models used in code generation is GitHub Copilot. It uses language models to provide real-time coding suggestions and generate complex programs, thereby improving developer efficiency.

4. Education and Professional Training

LLMs are becoming more important in the domain of education and training as they can offer personalized learning experiences. AI chatbots in the field of education can not only generate educational content but also provide personalized explanations. Language models can offer the benefit of adaptive learning systems that teach according to the expertise of learners.

5. Business Operations

With the consistently increasing levels of sophistication in deep learning models, LLMs will offer stronger foundation for improving productivity in business operations. LLM-based tools can help businesses address different issues, such as improving employee efficiency, summarizing meetings and automating routine, repetitive tasks. Language models will define the future of competitive advantage by facilitating workflow streamlining in different departments.

Curious about the real impact of AI chatbots on customer engagement and sales? Discover AI chatbot examples that increased conversions to learn how intelligent chatbots drive measurable results.

Do LLMs Have Limitations?

Yes, language models also have limitations such as lack of access to knowledge, computational resources, AI hallucination and biases. LLMs cannot deliver relevant responses when they don’t have the data required for pre-training or fine-tuning. At the same time, you cannot trust the responses of pre-trained LLMs which do not update their knowledge base.

Language models, especially the ones relying on deep learning, require high-end computational resources. As a result, implementing LLMs comes at a significant cost. On top of it, you cannot undermine the threat of AI bias and hallucinations that might lead to discriminatory or completely irrelevant output.

Transform Business Innovation with Large Language Models

The fundamentals of LLMs reveal that they are an integral component of the modern AI landscape. During the process of understanding large language models, you can learn how they work with the transformer architecture. On top of it, the introductory guide on LLMs revealed the essential concepts, such as context window, tokens and embeddings. Mindpath’s AI development services support businesses in applying LLM technology effectively to create intelligent solutions.

Discover the basics of Large Language Models (LLMs) and how Mindpath can help you build a customized AI solution to enhance efficiency and drive innovation.
Devops vs devsecops

DevOps vs. DevSecOps is a topic that will often arise when companies look for better and faster software delivery. Businesses are looking to release applications and software faster than ever, but they are also mindful of the growing sophistication of security threats. So where can businesses find the balance of speed and safety? This is where the transition from DevOps to DevSecOps comes into play; the need for speed is balanced with more stringent security requirements.

In today’s fast-moving digital age, the speed of development plays an important role, but it’s hardly enough. In addition to wanting systems that develop software quickly, organizations want systems that will also withstand vulnerabilities at each stage. That is why there’s so much interest in DevSecOps. DevSecOps does not replace DevOps; it enhances it by using continuous security assessments and ongoing protection. A clear understanding of these differences allows businesses to make better choices that can balance innovation with resilience. So, keep reading further to know the difference between DevOps and DevSecOps in this blog.

Still unaware of how DevOps benefits your business? Get in touch with us to gain full insight into adopting DevOps services that makes your operations seamless.

What is DevOps?

DevOps is a collaborative software development methodology that unites an organisation’s Development (Dev) and IT Operations (Ops) teams to deliver software faster, more reliably, and at greater scale. Its foundation is automation, continuous integration (CI), and continuous delivery (CD), commonly combined as CI/CD. DevOps helps break down silos between teams, enabling shared goals while reducing risk. It simplifies processes, improves team efficiency, and aligns technology outcomes with both customer and business objectives.

Furthermore, it drives a cultural change that values accountability, empathy, and shared responsibility. With automation, fast iterations, and rapid feedback, businesses are able to deliver secure and reliable software. In addition to this, not only does the process encourage innovation and creativity, but it also gives businesses flexibility and resilience in a competitive marketplace.

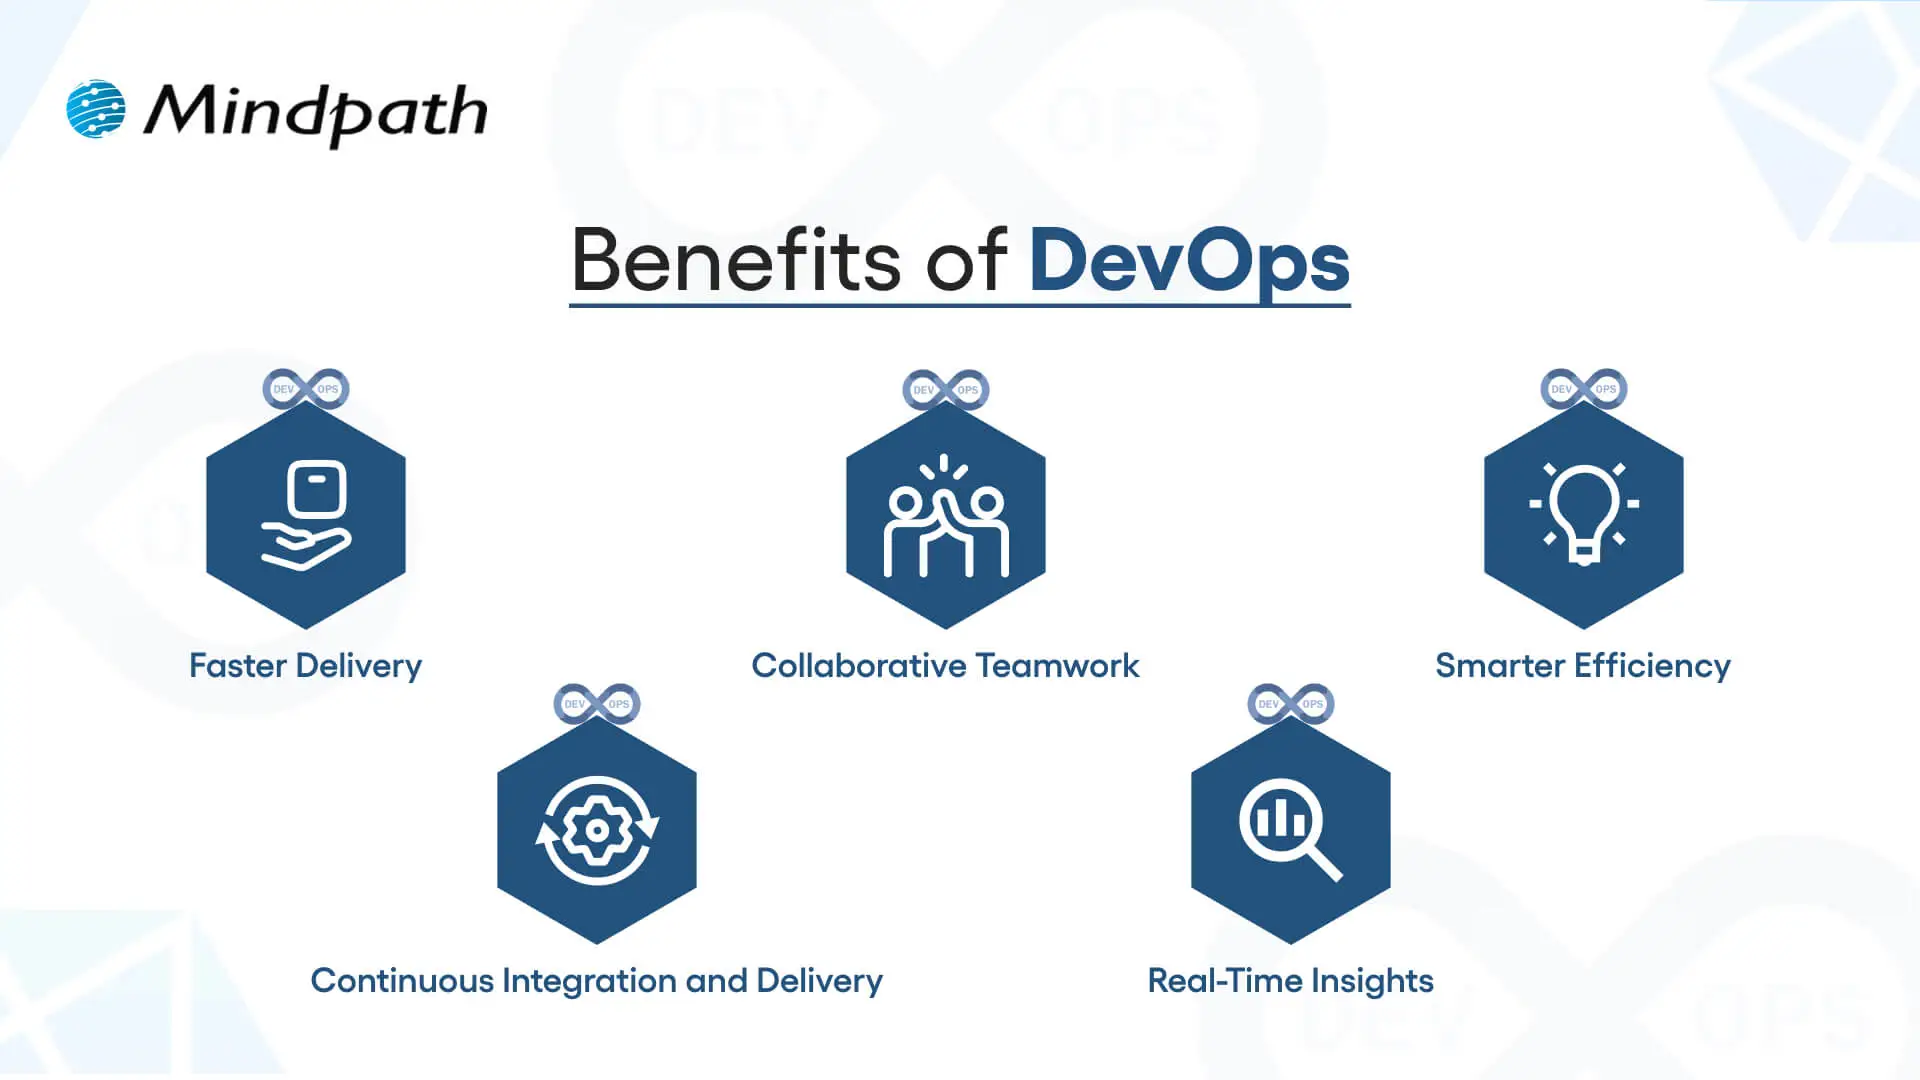
Here are some of the benefits of DevOps: 

1. Faster Delivery

Development cycles can go a lot quicker with automation and simplified processes. This enhanced delivery allows more frequent releases and decreases time to market.

2. Collaborative Teamwork

Development teams, operations, and other teams are all working toward common goals. Good team collaboration eliminates silos and improves project quality.

3. Smarter Efficiency

Automation eliminates repetitive tasks and optimizes workflows. Teams have the ability to save time and focus on activity that produces value, instead of spending time on manual processes.

4. Continuous Integration and Delivery (CI/CD)

Continuous integration and continuous delivery allow for reliable and consistent deployments. Your users can get new features and fixes fast and seamlessly.

5. Real-Time Insights

Monitoring tools enable instant visibility across the ecosystem. Teams can identify problems early, troubleshoot quickly, and improve performance.

These points explain how DevOps speeds up collaboration and delivery when comparing DevOps vs. DevSecOps, while DevSecOps extends an approach that has been inherently faster approach by adding stronger security practices.

Curious how automation and modern practices can improve your DevOps pipeline? Visit our blog on DevOps Trends to discover actionable insights and emerging innovations.

What is DevSecOps?

DevSecOps (Development, Security, and Operations) is the practice of integrating automated security checks into every phase of the software development lifecycle. It unites development, security, and operations teams so they can plan, build, test, and release applications together, making security a shared responsibility from the start. In return, DevSecOps allows for faster, more reliable processes, ensuring that security is built in from the very beginning rather than added as an afterthought.

To better understand the three pillars of DevSecOps, simply think of collaboration, automation, and continuous security. Collaboration ensures that everyone is sharing the responsibility, automation introduces automated security checks into CI/CD pipelines, and continuous security ensures that monitoring is continuous. With the three pillars of DevSecOps, organizations are able to create dependable applications while implementing continuous security measures to defend them against constantly evolving threats.

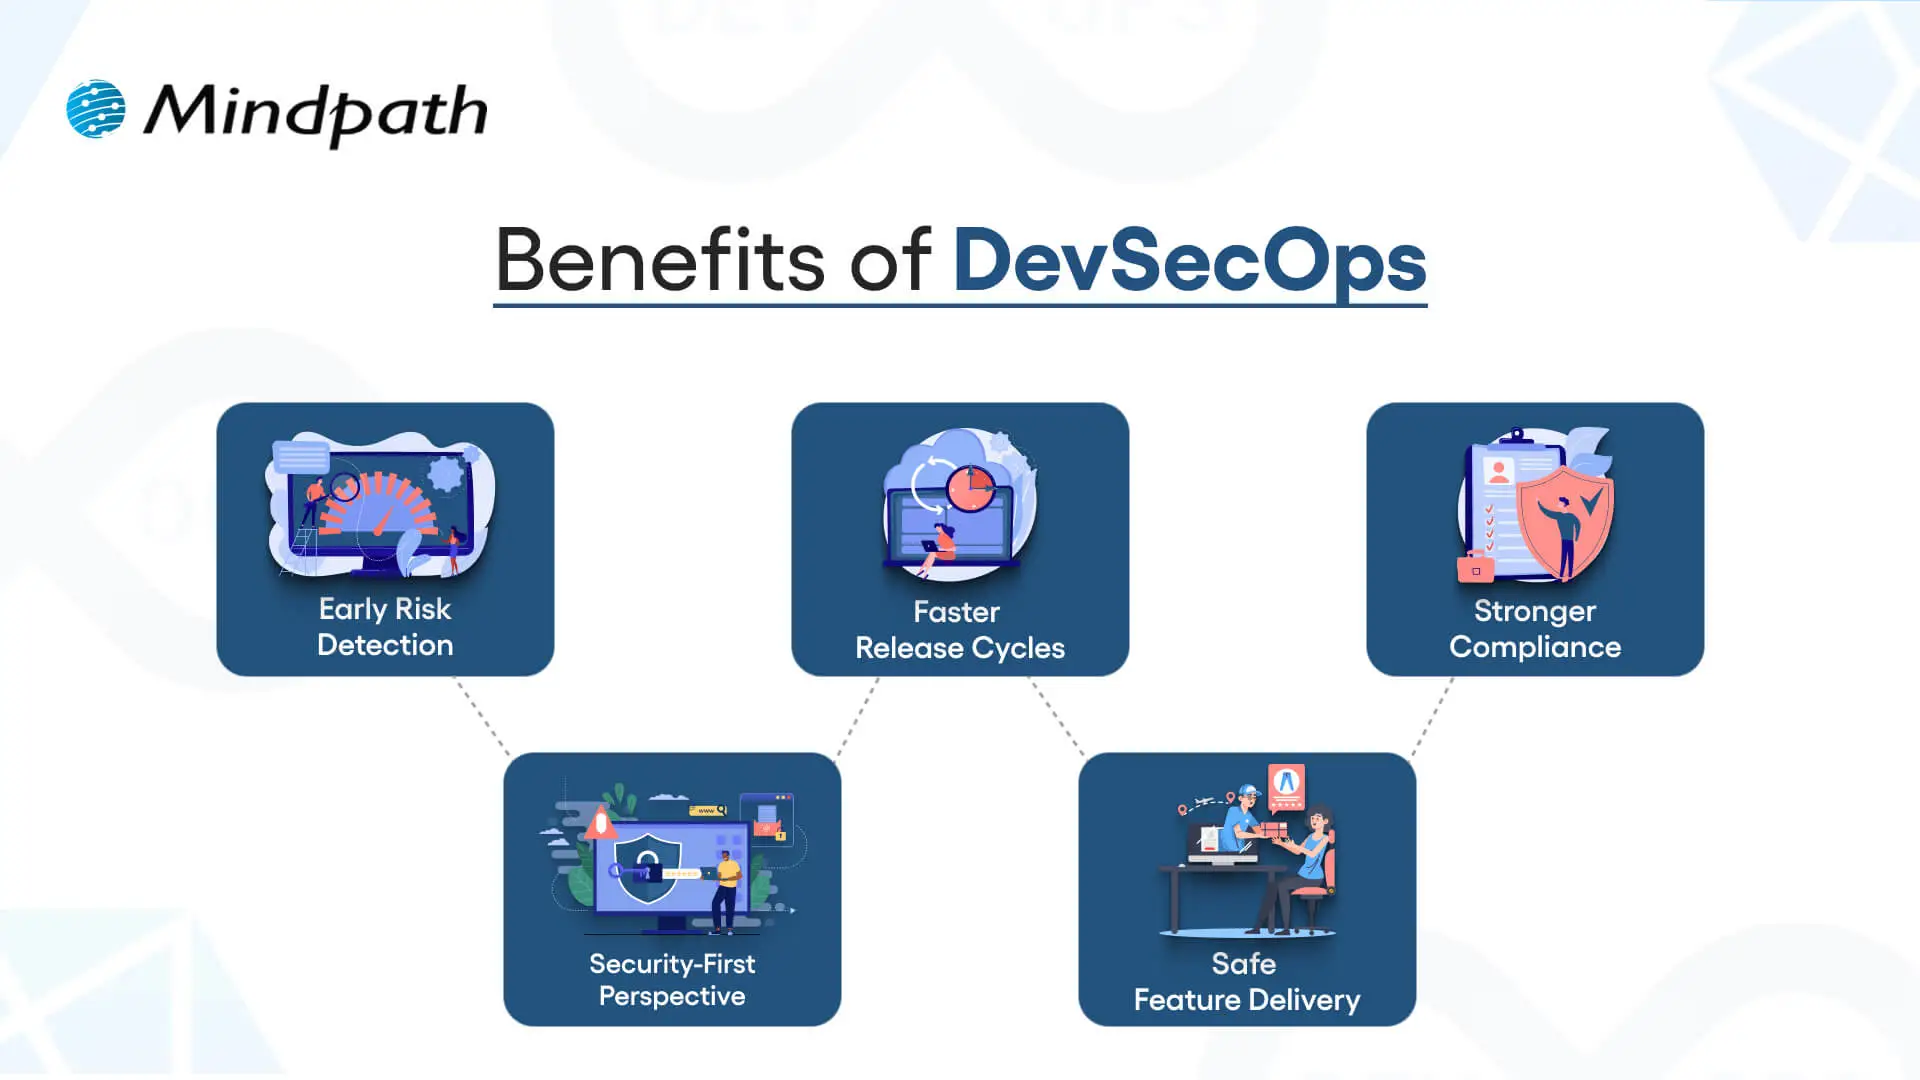
Here are the benefits of DevSecOps:

Benefits of DevSecOps

1. Early Risk Detection

DevSecOps allows for the identification of vulnerabilities during the development phase rather than at the end of the development process. Finding and remediating risk early in this way saves time and expense and means that users receive secure applications.

2. Faster Release Cycles

As teams can impact security testing in their workflow, delays are prevented, human error is removed, and developers get new features into the hands of users sooner.

3. Stronger Compliance

DevSecOps processing can assist software teams in meeting compliance obligations with strict regulatory guidelines. Automated checks and secure development practices ensure that data continues to be protected, while developers can be assured that they meet industry standards.

4. Security-First Perspective

Treating security as a shared responsibility, teams practicing DevSecOps have developers, security professionals, and operations staff collaborating to manage risks actively and ensure they minimize incidents throughout the development period.

5. Safe Feature Delivery

With DevSecOps, teams can deliver new functionality faster while also guaranteeing that security practices are undertaken throughout the development period. This can be one of the key differences in terms of DevOps vs. DevSecOps: how features are delivered.

Aiming to enhance operational efficiency and reduce development risks? Check out our blog on DevOps Challenges and Solutions to discover proven approaches that improve performance, stability, and cross-team cooperation.

DevSecOps vs. DevOps: Key Differences

DevOps vs. DevSecOps reveals how software teams value speed, teamwork, and security. While DevOps emphasizes faster delivery, DevSecOps enhances that process, making security a priority at every step of the development process.

1. Security Focus

The primary distinction between DevOps vs DevSecOps is security. DevOps puts movement between development and operations to speed up the delivery of software, but its security processes are usually significant afterthoughts. DevSecOps has security processes established from start to finish and considers them a core capability. By treating security as a core capability, vulnerabilities are eliminated upstream, so they are remedied before deployment.

2. Collaboration Culture

DevOps emphasizes collaboration between development teams and operations teams to promote continuous integration and delivery. Security is often treated as an independent effort, which creates holes in the development process. DevSecOps emphasizes the work of the security team interacting directly with developers and operations teams in every phase of development. This develops a culture of security being everyone’s responsibility.

3. Timing of Security

Conventional DevOps teams often include security at the final phase of the development cycle. If bugs occur towards the end of the process, they can delay the project significantly. DevSecOps reinforces timing by introducing a shift-left strategy with security at the beginning of the development process to build secure and reliable applications.

4. Tools and Automation

In contrast, when discussing DevOps vs. DevSecOps tools, the distinction is clear. DevOps follows automated processes for build, test, and deploy; however, normally, the security tools are still standalone. With DevSecOps, you use drive-by automated security scans, code analysis, and continuous monitoring in the CI/CD pipeline. It allows teams to detect threats in real-time without having to slow their delivery pace.

5. Salary Comparison

There is a notable salary gap when looking at DevOps vs. DevSecOps salaries in the UK. DevOps Engineers generally earn from £65,000 to £92,500+ with a difference based on skills and location, while DevSecOps Engineers receive a greater salary, with salaries for senior roles exceeding £130,000+ a year, particularly for positions based in London.

Looking to optimize your CI/CD pipeline with smarter automation and streamlined processes? Visit our blog on DevOps Best Practices to discover the strategies high-performing teams use to achieve consistent, stable releases.

DevOps vs. DevSecOps: A Comparison Table

When exploring DevOps vs. DevSecOps, it’s clear that both approaches aim to improve software delivery but take different routes to get there. This table highlights the main distinctions, making it easier to see how DevSecOps builds on DevOps with an added focus on security.

Aspect DevOps DevSecOps
Core Goal Focused on speeding up development and deployment cycles. Balances speed with security to deliver safe, reliable software.
Team Culture Collaboration between development and operations teams. Shared responsibility among development, operations, and security teams.
Security Approach Security checks are introduced late in the release pipeline. Security is integrated into every stage of the development lifecycle.
Automation Uses CI/CD pipelines to automate builds, tests, and deployments. Extends CI/CD with automated security scanning and compliance checks.
Risk Handling Issues are often fixed after vulnerabilities are found in production. Risks are identified and mitigated early to prevent breaches.
Compliance Handled towards the end of development, often as a final step. Built into processes from the beginning, ensuring continuous compliance.
Toolset Relies on monitoring, deployment, and collaboration tools. Adds tools for code analysis, threat detection, and policy enforcement.
End Result Delivers applications quickly but may leave gaps in security. Produces faster releases that are also secure, compliant, and resilient.

Which approach will drive your business forward?

The comparison of DevOps vs. DevSecOps shows that while DevOps accelerates delivery, DevSecOps ensures that speed is not achieved at the cost of security. Businesses gain the ability to innovate quickly while reducing vulnerabilities. Choosing the right model depends on priorities, but integrating security early always results in stronger, more resilient software outcomes.

At Mindpath, we offer tailored DevOps services designed to improve speed, collaboration, and reliability across your software delivery cycle. By helping teams embrace automation, modern practices, and security-focused strategies, Mindpath ensures that businesses not only accelerate development but also deliver secure, high-performing applications that stand out in today’s competitive digital market.

remote work security

Remote work security refers to the practices, technologies, and policies that protect corporate data and networks when employees work outside a traditional office environment. Teams operate across devices, networks, and locations every day, and without corporate firewalls in place, even small gaps can create serious vulnerabilities. The risks evolve quickly, which is why businesses need protection strategies built on strict user verification, encrypted network connections, and continuous endpoint monitoring without disrupting daily workflows or user experience.

Decisions on security must be clear and consistent as organizations increase remote setups. Leaders need to pose the correct questions and take actions. Meanwhile, employees require straightforward and easy to use systems that facilitate day-to-day operations. Consequently, there is a need to have a balanced approach to succeed in the long term. This blog will provide explanations of important aspects of remote work cybersecurity in a clear and practical manner. So, keep reading further!

Ready to secure your remote workforce and protect your business from evolving cyber threats? Contact us to explore how our team can help you build a safer and more resilient remote work environment.

The Growing Cyber Risk in Remote Work Environments

Not only in the office, remote work also faces rising cyber threats today. Remote work security is vital because employees are using their personal networks and devices to access systems. These are some of the weak points that hackers attack. Consequently, minimal security breaches have the potential to compromise business information and interrupt routine business activities within a short time.

Simultaneously, remote workforce cybersecurity is exposed to increasing threats as the techniques of attacks advance daily. Phishing, ransom, and identity attacks are growing at a high rate. Remote setups are fast to adapt to cybercriminals. Thus, organizations need to remain vigilant and increase security to manage these changing threats.

Want to better understand how to scale teams without increasing security risks? Explore the benefits of hiring remote developers to balance flexibility with control.

Here are some of the remote workforce security risks:

1. Unsecured Network Risks

At home or cafes, employees tend to connect to unsecured networks. These connections can easily be intercepted by attackers to get sensitive data.

2. Weak Password Security Risks

A large number of users use the same password on several accounts. A single breach may reveal multiple systems within a short time.

3. Personal Device Security Risks

Individual gadgets frequently lack frequent security patches and safeguards. This provides malware and attacks with easy entry points.

4. Phishing and Social Engineering Risks

To deceive users, hackers use spoofed emails, or messaging. Such attacks seek to steal usernames or confidential information.

5. Shadow IT Security Risks

Employees sometimes use apps without company approval for convenience. This bypasses security controls and increases risk.

6. Software Update Security Risks

Remote devices might not get security patches in a timely manner. This exposes systems to well-known threats and vulnerabilities.

7. Physical Security Risks

The devices may be lost or found in high-traffic or communal areas. Critical business information may be put at risk as a result of unauthorized access.

Looking to simplify how your remote teams stay connected and secure daily? Discover powerful remote work tools that support safer collaboration.

Importance of Cybersecurity in Remote Work

Remote work security is key in safeguarding data and systems when working remotely. Here are the reasons why solid cybersecurity is still needed in the daily remote work setting.

1. Protecting Expanding Digital Entry Points

Remote work adds devices, networks and points of access to systems. Cybersecurity for remote work helps control risks in these expanded environments.

2. Securing Sensitive Business Data

Every day, employees gain access to and share crucial information that is not secured by office infrastructure. Work from home security will also protect data when storing and transferring data.

3. Reducing Phishing and Online Fraud Risks

Users who are distantly located are faced with rising phishing attacks in the form of emails and fraudulent communications. High level of security awareness will avoid unintentional sharing of sensitive login information.

4. Maintaining Strong Security Standards

Both personal and shared devices may not have consistent security updates and protection tools. The use of consistent policies guarantees similar protection standards across all systems.

5. Ensuring Business Continuity

Cyber attacks have the ability to interrupt workflow and slow down processes happening remotely. Good security control mechanisms assist in stability and prompt recovery exercises.

6. Building Trust and Meeting Compliance

Data security breaches may destroy reputation and decrease customer confidence within a short time. Adequate security would keep the rules and guard business reputation.

Planning to strengthen your security foundation as your business grows? Read about application security best practices to protect your systems effectively.

Cybersecurity Best Practices

Remote working security requires effective habits to safeguard information and systems in remote configurations. These are the best practices that can be implemented in order to enhance safety and minimize risks.

1. Safe Network Access (VPN Use)

Connect with secure VPN to all remote work activities on a daily basis. This secures information transfer among the commonly shared and open internet systems.

2. Home Network Protection

Protect home routers by using strong passwords and updating encryption parameters. Store smart devices on different networks to minimize security risks.

3. Timely Software Updates

Automatically update all systems and security applications. Frequent patches seal identified vulnerabilities and thwart cyber attacks in real-time.

4. Stronger Login Protection (MFA)

Implement several authentication measures whenever accessing the company system. Remote work security enhances safety of access via additional authentication measures.

5. Strong Password Management

Use different passwords on each account using secure password tools. Do not use the same passwords in personal and work accounts.

6. Employee Security Awareness

Train employees on how to detect phishing emails and suspicious online activities. Establish a powerful security culture to avoid unintentional data breaches.

Is Your Organization Truly Ready for Strong Remote Workforce Security?

Remote work has transformed the way teams work and exchange information on a daily basis. Powerful Remote Work Security assists in safeguarding information, hardware, and networks during the increase in cybercrime. It guarantees safer communication, stronger control, and minimized risks in the distributed work setting in the long term business stability and trust.

At Mindpath, we offer remote work security solutions to secure modern distributed teams with robust, trustworthy systems. Our strategy revolves around safe access, data security and risk mitigation. We assist companies to create secure remote working environments that do not affect productivity at all.

Learn essential cybersecurity practices for remote work and how Mindpath can help protect your business with expert solutions.